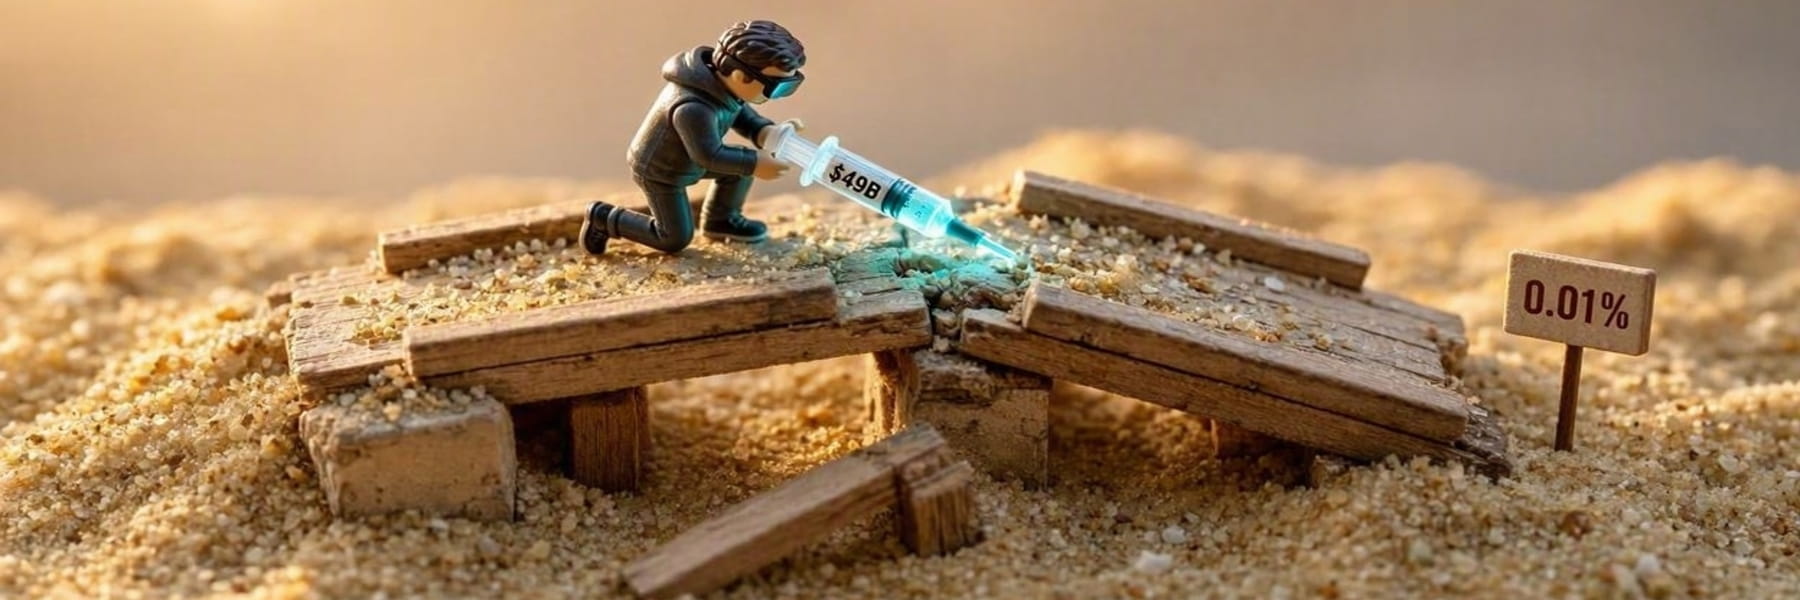
The Sandbox, a leading metaverse and blockchain gaming platform, suffered a major security breach on August 22 when an attacker exploited a vulnerability in its cross-chain bridge infrastructure on Base and BNB Smart Chain. The hacker hijacked LayerZero delegate permissions through an approveAndCall function on the SAND omnichain fungible token contract, then minted unbacked SAND tokens on both networks. Security firm Blockaid flagged the exploit while it was still underway and estimated that approximately $49 billion in face-value SAND was minted across more than 400 transactions.
PeckShield separately counted 14.9 billion SAND minted across two addresses. However, the Sandbox team emphasized that the actual financial impact was minimal—the attacker drained only about 14.75 million SAND from the Ethereum backing contract, converting it to roughly 80 ETH valued at approximately $675,000. The company immediately halted bridging on Base and BNB Smart Chain, isolated the affected tokens, and confirmed that Ethereum and Polygon SAND remained unaffected. The Sandbox stated that the incident affected less than 0.01% of SAND's total token supply and plans to compensate affected liquidity providers. The incident highlights ongoing concerns about blockchain security, where the integrity of peer-to-peer transactions relies on public and private cryptographic keys. Data availability remains crucial to blockchain integrity, security, and functionality, with distributed data across multiple nodes making the network more resilient to attacks.